Skip to the main content
{}

Laravel maintenance and application takeover

Laravel maintenance or a controlled application takeover.

Need Laravel maintenance, replacing a developer or dealing with a difficult codebase? Codegenie maps the application and production context and prepares a plan for takeover, stabilisation and focused follow-up before larger changes.

From existing access to clear maintenance responsibility.

A takeover starts by understanding what the business needs. Begin with an inventory and agreed investigation, then maintenance or changes. A focused audit can be the first step; an acute blocker may need a separate rescue engagement.

Inventory: access, environment and risks

Identify owners of the repository, hosting, database and external accounts. Record setup, deployment, backups, known incidents and missing documentation. Access or test data is shared only through an agreed safe channel.

Explore the scoped audit/rescue
Document critical flows clearly

Together with users, select the actions that must keep working and describe normal steps, exceptions and access rules. Connect known problems to those flows and a check before and after a change.

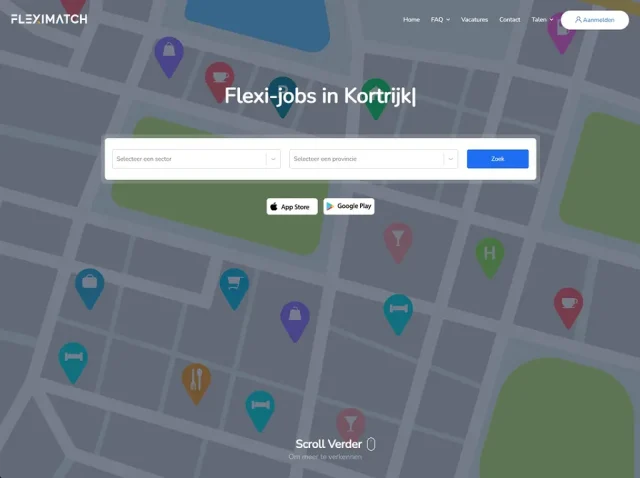
FlexiMatch documents separate onboarding and matching for two roles. This is evidence of a delivered application flow, not a client takeover. It helps illustrate the behaviour maintenance needs to preserve.

Explore the FlexiMatch role example

Illustrative handover record

A record could list the owner, required access, critical flow, check, risk and next action for each area. Define who deploys, handles incidents, checks backups and approves further work. This is an illustrative record, not a published client delivery report; ongoing management and capacity are agreed separately.

Discuss takeover and ongoing management

Which Laravel service fits your question?

Each page has one primary intent: hire a Laravel developer, build a new application, maintain or take over existing Laravel software, or run a focused audit/rescue. This keeps each engagement clearly scoped.

What the work includes

01

Access and ownership

Assign ownership of the repository, hosting, database, domain and external accounts. Share access through an agreed secure channel, not a public issue or initial contact form.

02

Understand critical flows

Identify the user actions the business depends on, integrations and failure behaviour. Existing tests and a reproducible development environment are the starting point.

03

An actionable handover plan

Separate blockers, immediate risks, maintenance and deferred improvements. Each finding explains its relevance and how a proposed change can be checked.

04

Responsibilities after handover

Agree who deploys, handles incidents, manages access and approves future work. A temporary intervention is not automatically an unlimited maintenance contract.

Unfamiliar code is not a reason for a rewrite

A Quick Audit can be the first bounded step. Then choose maintenance, focused stabilisation, temporary capacity or a larger improvement.

  • 01No broad dependency updates before compatibility and impact are understood.
  • 02No production intervention without suitable access, backup and recovery arrangements.
  • 03No 24/7 availability or full recovery promised without a separate agreement.

Is the delay in Laravel or in the database?

A slow application does not automatically need a rebuild. When repeated relationship queries, heavy reports or unsuitable indexes cause the problem, focused SQL analysis can be the right next step. First establish where the delay originates.

Approach

From brief to delivery

Scope and responsibilities are clarified first. We then build and verify the solution in controlled steps.

  1. Access

    Define authority, repository and environments.

  2. Inventory

    Inspect critical flows, dependencies, data and deployment.

  3. Plan

    Prioritise blockers and recommended maintenance by impact.

  4. Transfer

    Hand over changes, documentation and operational responsibility.

Frequently asked questions

Can you start without documentation?

First examine what the repository, configuration, tests and behaviour reveal. Missing context and access remain explicit estimation risks.

Does the previous developer need to help?

A handover helps, but available rights and information determine what is possible. The customer must be authorised to have the code and accounts examined.

What follows the audit?

A prioritised handover plan and proposed next step. An audit does not itself authorise broad changes or a complete rebuild.

Need a controlled Laravel handover?

Describe the application, available access and known problems. Do not include secrets in the brief.